Data protection

Access, correction, erasure: the rights look similar the world over. What differs is whether anyone enforces them.

Illustration: Data protection

Appear on this page

Get our daily news watch

One model, widely exported

Most recent data protection statutes share a blueprint: a lawful basis for every use, transparency obligations, data minimisation and purpose limitation, rights of access, correction, erasure, objection and portability, breach notification, and an independent regulator. That design spread outwards from Europe and has been adopted, sometimes almost word for word, across very different legal traditions.

The real difference is enforcement

On paper the rights are close to identical. In practice what counts is whether a regulator exists, whether it has staff and the power to fine, and whether it uses them. Some countries have a statute with no functioning authority behind it; others have an authority issuing substantial penalties. A third difference is routinely overlooked: whether government bodies are covered at all — several statutes exclude them expressly.

Compensation is the exception
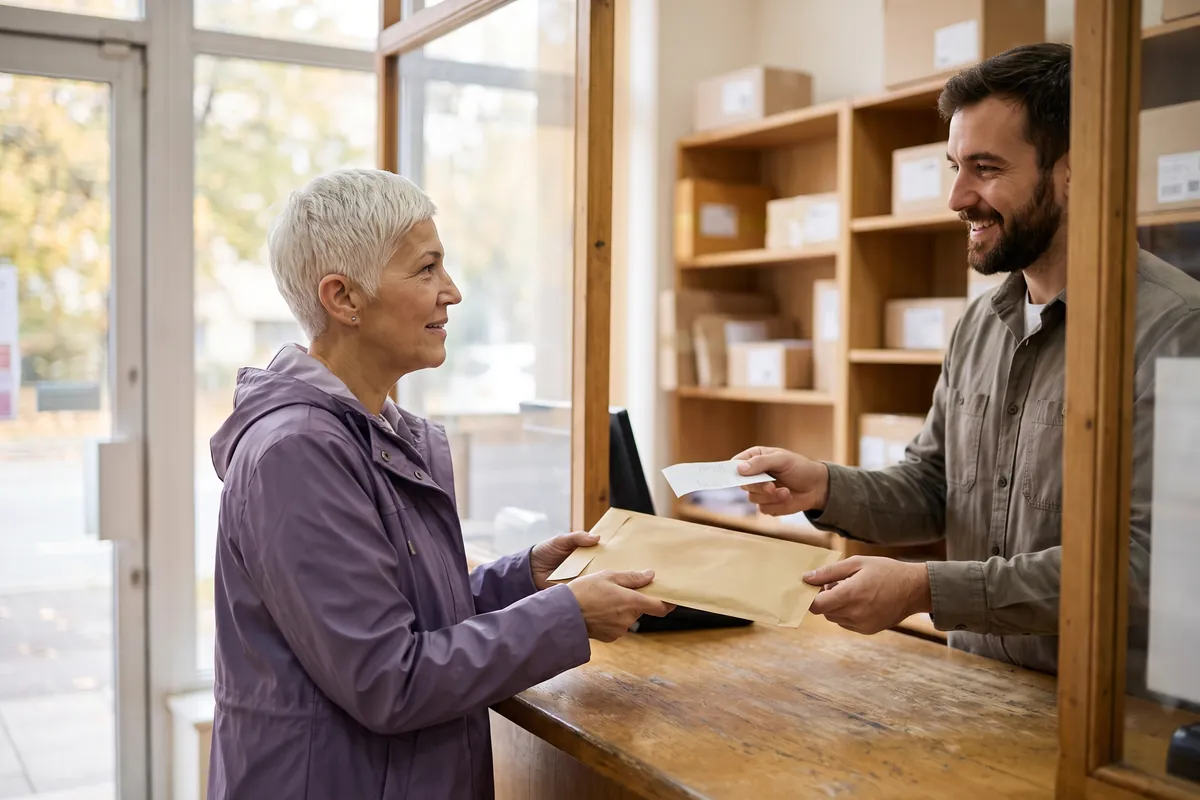
A woman in her sixties hands an envelope over a post office counter and receives a receipt
An access request takes a few lines: date it and keep proof of sending.

Many statutes provide penalties payable to the state but no personal right to damages. Where such a right exists, courts generally require demonstrable harm; the breach alone is not enough. If you want compensation, start documenting the consequences for you from the first day — not the breach, the consequences.

The access request is the most effective tool

It is usually free, requires no reason, and forces the other side to disclose what it holds, where it came from and who it was shared with. Response deadlines are typically a month. The answer is also the foundation for anything that follows, which is why an access request belongs at the beginning of a dispute rather than at the end.

In writing, and dated

Send requests in writing with proof of delivery and keep that proof. Without a date you cannot later show that the deadline passed — and it is precisely that missed deadline that gives a regulator something to act on.

The law country by country

The legal framework, the procedure, the time limits and the costs differ from one country to another. Each country below has a detailed page: governing texts, key facts, the actual procedure, costs, where to go and the traps to avoid.

Select a country to open its detailed page.
European framework

European Union

The GDPR is a regulation: it applies directly in all twenty-seven member states without transposition, and it turned data protection into an enforceable individual right.

Europe

Ireland

GDPR enforced by a Data Protection Commission that acts as lead regulator for much of the global tech industry.

Spain

The GDPR and Organic Law 3/2018 (LOPDGDD) apply, with the Spanish Data Protection Agency (AEPD) as regulator — one of Europe's most active, fines up to 20 million euros or 4 % —, the digital age of consent at 14, a priority channel to remove non-consensual intimate images within hours, and an offence (article 197.7 of the Penal Code, 3 months to 1 year) for sharing them; UK residents keep GDPR-level rights against Spanish companies.

United Kingdom

UK GDPR and the Data Protection Act 2018, enforced by the Information Commissioner, with a free complaints route.

Western Africa

Ghana

The Data Protection Act 2012 is administered by the Data Protection Commission, and registration of data controllers is its distinctive feature.

Nigeria

The Nigeria Data Protection Act 2023 created the Nigeria Data Protection Commission, with registration for major data controllers.

Middle Africa

Cameroon

Cameroon protects personal data through Law No. 2024/017 of 23 December 2024, in force since 23 June 2026: it creates an independent Personal Data Protection Authority (APDP), grants rights of access, rectification, objection and erasure, and makes transfers abroad subject to prior authorisation; Law No. 2010/012 on cybersecurity and cybercrime, applied by the ANTIC (the national information and communication technology agency), still covers online offences. Against organisations in the UK or the EU, the UK GDPR or the GDPR protects you wherever you live; and since Cameroon has no adequacy decision from the UK or the EU, transfers of personal data there need extra safeguards.

Eastern Africa

Ethiopia

The Personal Data Protection Proclamation No. 1321/2024 gives individuals rights of access, correction, erasure and objection, requires controllers to register with the Ethiopian Communications Authority and notify breaches within 72 hours, and punishes selling personal data with five to ten years or a fine of 200,000 to 600,000 Birr (Art. 64(3)).

Kenya

The Data Protection Act 2019, modelled closely on the GDPR, is enforced by a Commissioner's office that has issued penalty notices.

Rwanda

Law N° 058/2021 of 13/10/2021 covers any processing of personal data of people in Rwanda, requires controllers and processors to register with the supervisory authority, asks for a parent's consent for a child under 16, gives rights of access, objection, erasure and rectification (the last three answered within 30 days), and punishes unlawful sharing of data with one to three years and a fine of FRW 7 million to 10 million.

Tanzania

The Personal Data Protection Act, 2022 (Cap. 44) requires every collector of personal data to register with the Personal Data Protection Commission, gives individuals rights of access, objection and compensation, lets the Commission fine up to TSh 100 million (s. 47) and punishes unlawful disclosure or sale of personal data with up to ten years (s. 60).

Uganda

The Data Protection and Privacy Act 2019 gives rights of access and correction, overseen by the Personal Data Protection Office.

Zambia

The Data Protection Act 2021 sets a full framework with registration of data controllers, and the regulator is still building capacity.

Southern Africa

South Africa

South Africa’s POPIA sets conditions for using personal information. Electronic marketing has specific consent rules, including a limited exception for existing customers.

Southern Asia

India

The DPDP Act 2023 became operational when its Rules were notified in November 2025, with obligations phased in to 2027.

Pakistan

No comprehensive data protection statute yet: protection rests on cybercrime legislation and sectoral rules.

Eastern Asia

Hong Kong

The Personal Data (Privacy) Ordinance, with six data protection principles and a doxxing offence added in 2021.

South-eastern Asia

Indonesia

Law No. 27 of 2022 on Personal Data Protection gives people rights of access, correction, deletion and withdrawal of consent, sets three-day deadlines for controllers (Arts. 30, 32 and 40), fines of up to 2% of annual income (Art. 57(3)) and up to five years' prison for unlawfully obtaining another person's data (Art. 67(1)); its two-year adjustment period ended on 17 October 2024 (Art. 74).

Malaysia

The PDPA 2010, significantly amended in 2024 with breach notification, data protection officers and portability.

Philippines

The Data Privacy Act 2012, enforced by an active National Privacy Commission, with criminal penalties for unauthorised disclosure.

Singapore

The PDPA with consent, purpose limitation and a Do Not Call registry, plus mandatory breach notification since 2021.

Northern America

Canada

PIPEDA federally, provincial statutes in three provinces, and Quebec's Law 25 as the strictest regime in North America.

United States

No comprehensive federal privacy law: sectoral federal rules, an expanding patchwork of state statutes, and FTC enforcement.

Caribbean

Jamaica

The Data Protection Act 2020 follows the GDPR structure with eight standards, enforced by the Information Commissioner.

Trinidad and Tobago

The Data Protection Act 2011 is only partly proclaimed, so some provisions are in force and others are not.

South America

Argentina

Law 25.326 on the protection of personal data (2000), recognised as adequate by the European Union, gives rights of access, rectification and deletion and the constitutional action of habeas data (article 43), with the Agencia de Acceso a la Información Pública (AAIP) as regulator and modest fines; sharing intimate images has been digital violence since Law 27.736 (2023), with no specific criminal offence except where minors are involved; a new law is still before Congress. Personal data can flow from the UK and Ireland to Argentina without special safeguards.

Oceania

Australia

The Privacy Act 1988 with thirteen Australian Privacy Principles, mandatory breach notification, and reforms introducing a privacy tort.

New Zealand

The Privacy Act 2020, with thirteen principles, mandatory breach notification and an unusually accessible complaints process.

This topic is also covered for French-speaking countries · German-speaking countries · Spanish-speaking countries · Italy and Italian-speaking Switzerland · Portuguese-speaking countries · the Netherlands, Flanders and Suriname · Poland and the Polish diaspora · Türkiye and the Turkish diaspora.

Sources

  1. Donnée personnelle — French Data Protection Authority (CNIL), accessed 2026 (in French): any information relating to an identifiable person, directly or by combining data: IP address, voice, image, fingerprints
  2. Règlement (UE) 2016/679 (RGPD), chapitre I : dispositions générales (art. 1 à 4) — French Data Protection Authority (CNIL), 2016 (in French): art. 4: data identifying a person directly or indirectly; art. 3(2): applies to services offered to people in the Union
  3. Règlement (UE) 2016/679 (RGPD), chapitre II : principes (art. 5 à 11) — French Data Protection Authority (CNIL), 2016 (in French): arts 5 (purpose, minimisation, storage limitation, security, transparency), 7(3) (withdrawal of consent at any time), 9 (special categories, explicit consent)
  4. Règlement (UE) 2016/679 (RGPD), chapitre IV : responsable du traitement et sous-traitant (art. 24 à 43) — French Data Protection Authority (CNIL), 2016 (in French): arts 32 (security), 33 (breach notified to the authority within 72 hours) and 34 (individuals informed when the risk is high)
  5. Règlement (UE) 2016/679 (RGPD), chapitre III : droits de la personne concernée (art. 12 à 23) — French Data Protection Authority (CNIL), 2016 (in French): arts 12 (reply within one month, free of charge), 15 (copy and recipients), 17 (erasure and its limits), 20 (portability), 21 (objection to direct marketing)

Official or institutional documents this page relies on, consulted on 12 October 2026. Links open in a new tab.

Content updated in . The instruments cited can change: if in doubt, confirm with the official source given.

Text written with the help of AI, under the editorial responsibility of CAPIT; human reviews are occasional (method and sources: About). This content does not replace medical or legal advice. Spotted an error? Write to us.

Locate this page in the site map